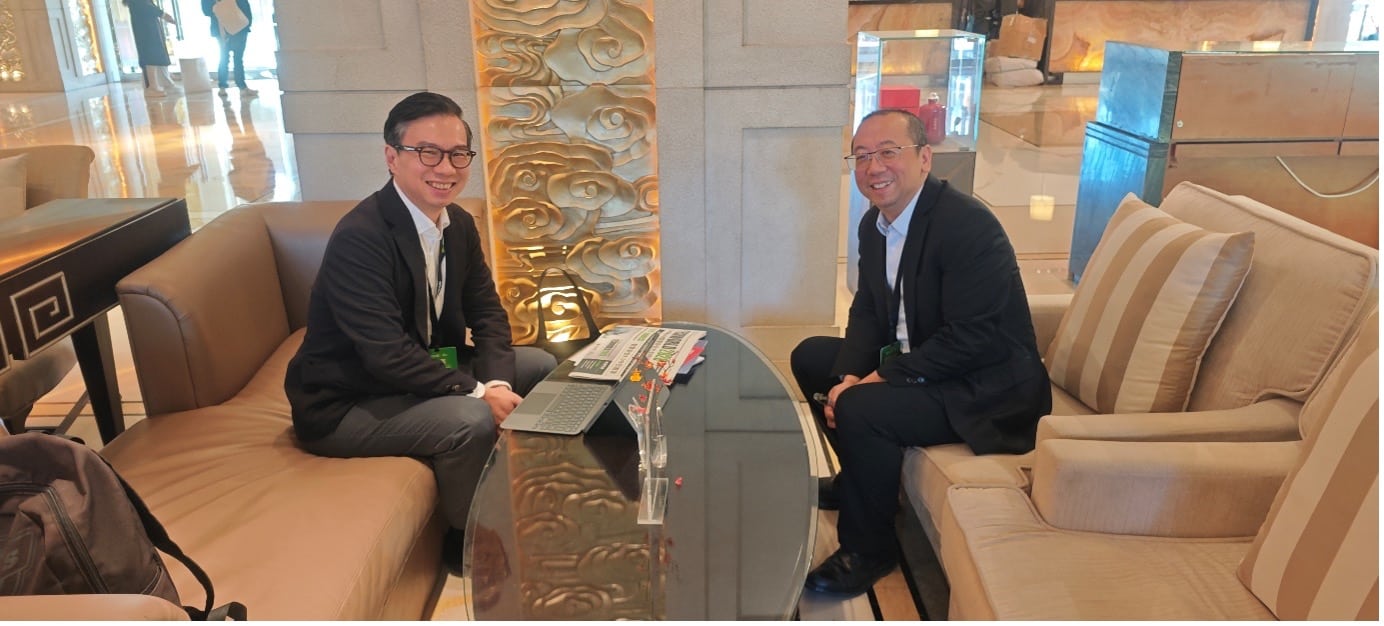
Dr. Xiaohu Ye, Chief Technology Officer of NSFOCUS, shares his views on how security teams can keep pace as AI accelerates attacks.
Artificial intelligence (AI) has quickly moved from novelty to everyday utility in both our personal and working lives. Frost & Sullivan’s Global State of AI research finds that nearly 90% of IT and business decision-makers recognize AI and machine learning as critical to achieving their business objectives, with deployments expanding from isolated use cases to enterprise-wide implementation. AI is also evolving fast, from systems that respond to individual requests to AI agents that work independently to fulfill an objective. As our security team observed at RSAC 2026, cybersecurity has now entered the agentic AI era.
That shift cuts both ways. AI is helping attackers discover and exploit vulnerabilities faster, just as the volume of vulnerabilities reaches new highs: a record 48,185 CVEs were published in 2025, a 20.6% increase over 2024, according to an annual review of CVE data. Add increasingly complex IT environments and growing regulatory demands, and the divide between attackers and defenders is widening. Yet for many organizations, the real gap is not visibility but judgment: knowing what matters and when to act.
These challenges were front and center at NSFOCUS TechWorld 2026. I sat down with Dr. Xiaohu Ye, Chief Technology Officer of NSFOCUS, to discuss what they mean for security leaders and where organizations should focus next. In his view, AI is now everywhere, attackers are using it too, and security must become more intelligent and proactive. That calls for three shifts: changing the objective from preventing every breach to assuming breach, making offensive testing and security operations continuous, and moving beyond detection toward active and predictive defense.
1. Change the objective: from preventing every breach to assuming breach
As AI becomes embedded in business operations and moves toward autonomous agents, Dr. Ye argues that the starting point is not a new tool but a new objective. For years, many security programs were built around a simple goal: prevent anything from happening. With AI accelerating attacks and tilting the balance in favor of attackers, that goal is no longer realistic.
“The objective of the security team has to change,” says Dr. Ye. “It is no longer realistic to expect to stop every attack. We have to assume breach and focus on how quickly we can detect an attack, so that we reduce the level of risk and the losses when it does happen.”
In practice, an assume-breach mindset puts the spotlight on metrics such as mean time to detect (MTTD), because faster detection directly limits the damage an intruder can do. It also requires organizations to raise their overall security maturity across all three pillars: technology, people, and processes.
Scale is the other pressure point. Security has historically depended on people and their expertise, but amid a growing workload and rising demand, that model no longer scales. Dr. Ye sees a new division of labor in which security professionals use AI agents to handle routine alerts and identification, while human experts concentrate on the complex issues that require judgment.
“Security used to be built on people and expertise, and that is simply not scalable anymore,” he explains. “To evolve into our next stage, embracing autonomous SOC is essential. Let the AI agents take care of the routine alerts and identification, and bring in human expertise for the complex issues.”
To evolve into our next stage, embracing autonomous SOC is essential.
— Dr. Xiaohu Ye, CTO, NSFOCUS
2. Close the gap: make offensive testing and security operations continuous
If organizations must assume breach, the next question is how quickly they can find their own weaknesses. Attackers are using AI to speed up every stage of an attack, particularly vulnerability discovery and exploitation, so Dr. Ye’s advice for defenders is to start with a clear, current understanding of their own vulnerabilities, and to detect them faster than adversaries can.
That has direct implications for penetration testing. Traditional engagements are periodic, labor-intensive, and constrained by the availability of skilled testers, while business systems change weekly or even daily. A point-in-time test quickly becomes outdated.
“You cannot close the gap with attackers if you only test yourself occasionally,” says Dr. Ye. “Penetration testing needs to be continuous, and we cannot rely on humans alone to do it. It has to be automated and AI autonomous, so you understand your real exposure before the attackers do.”
According to Dr. Ye, the value of AI autonomous penetration testing goes beyond speed. Effective testing should:
- Put vulnerabilities in business context, so teams understand what a weakness actually means for critical processes and data.
- Use different attack approaches, reflecting how real adversaries probe and chain weaknesses rather than following a fixed checklist.
- Reflect the actual production setup, customizing tests to how systems are deployed in the field.
- Fully test defensive capabilities, validating whether controls hold up, not simply producing a list of findings.
The same logic applies to security operations (SecOps). Many teams still effectively operate on a 5×8 basis, five days a week and eight hours a day, while attackers work around the clock. For Dr. Ye, that coverage is no longer sufficient.
“Attackers do not keep office hours, so security operations cannot either,” he notes. “SecOps needs to be continuous, and that is not achievable by adding more people alone. AI agents will work alongside SecOps analysts to help them keep up.”
3. Move beyond detection: build an AI security platform for active and predictive defense
Continuous testing and around-the-clock operations will surface more findings, not fewer, and that brings the judgment gap back into focus. With complexity rising on every front, from sprawling hybrid environments to an expanding body of regulation, Dr. Ye stresses that discovering threats and vulnerabilities is only the first step. The real goal is to reduce risk, moving from passive defense to active risk reduction and, ultimately, to predictive defense.
“Finding a vulnerability or detecting a threat is only the beginning,” says Dr. Ye. “Security has to move from passive to active risk reduction, and ultimately to predictive defense, where we can anticipate risks and act before they become incidents.”
Asked what the first important step should be, his answer is pragmatic: create an AI security platform and give it context across the environment. AI is only as useful as what it can see, so the platform needs visibility into the organization’s assets, vulnerabilities, and activity. From there, he recommends a staged journey:
- Establish the foundation. Create the AI security platform and connect it to context from across the environment.
- Start with the basics. Use AI for practical, lower-risk functions, such as helping security teams find answers faster.
- Progress to advanced capabilities. Build toward faster detection and fully testing vulnerabilities, turning insight into active risk reduction.
“The first step is to create your AI security platform and provide it with context across your environment,” Dr. Ye advises. “Start with the basic functions, then build from there.”
As organizations build out that platform, Dr. Ye stresses that the AI itself must be fit for purpose. In his view, security-specific models can be smaller than general-purpose large language models while delivering similar performance at a lower token cost, an important consideration as AI usage scales across the security stack. Just as important is continued research to improve detection accuracy in real-world production environments and field deployments, not just in the lab.
The road ahead
The message from NSFOCUS TechWorld 2026 and my conversation with Dr. Ye is clear: AI is changing the economics of cybersecurity for attackers and defenders alike. Organizations that continue to rely on periodic testing, manual triage, and a “prevent everything” mindset will find the divide widening. Those that assume breach, make testing and operations continuous, and invest in a context-rich AI security platform will be better placed to close the judgment gap and shift from reacting to incidents toward anticipating them.
For security leaders, the question is no longer whether to bring AI into their defenses, but how quickly they can build the foundation, and the trust, that allows AI and human expertise to work together.
About NSFOCUS
[NSFOCUS is an cyber security company with 23+ years of proven industry experience. Today, we are operating globally with 3000+ employees at two headquarters in Beijing, China and 50+ offices worldwide including the IBD HQ in Milpitas, CA, USA. NSFOCUS protects four of the ten largest global telecommunications companies and four of the five largest global financial institutions.]