This blog is based on Frost & Sullivan’s analysis, Frost Radar™: Cloud Workload Protection Platforms, 2026, authored by Anh Tien Vu from the Security Practice Area.
Executive Summary
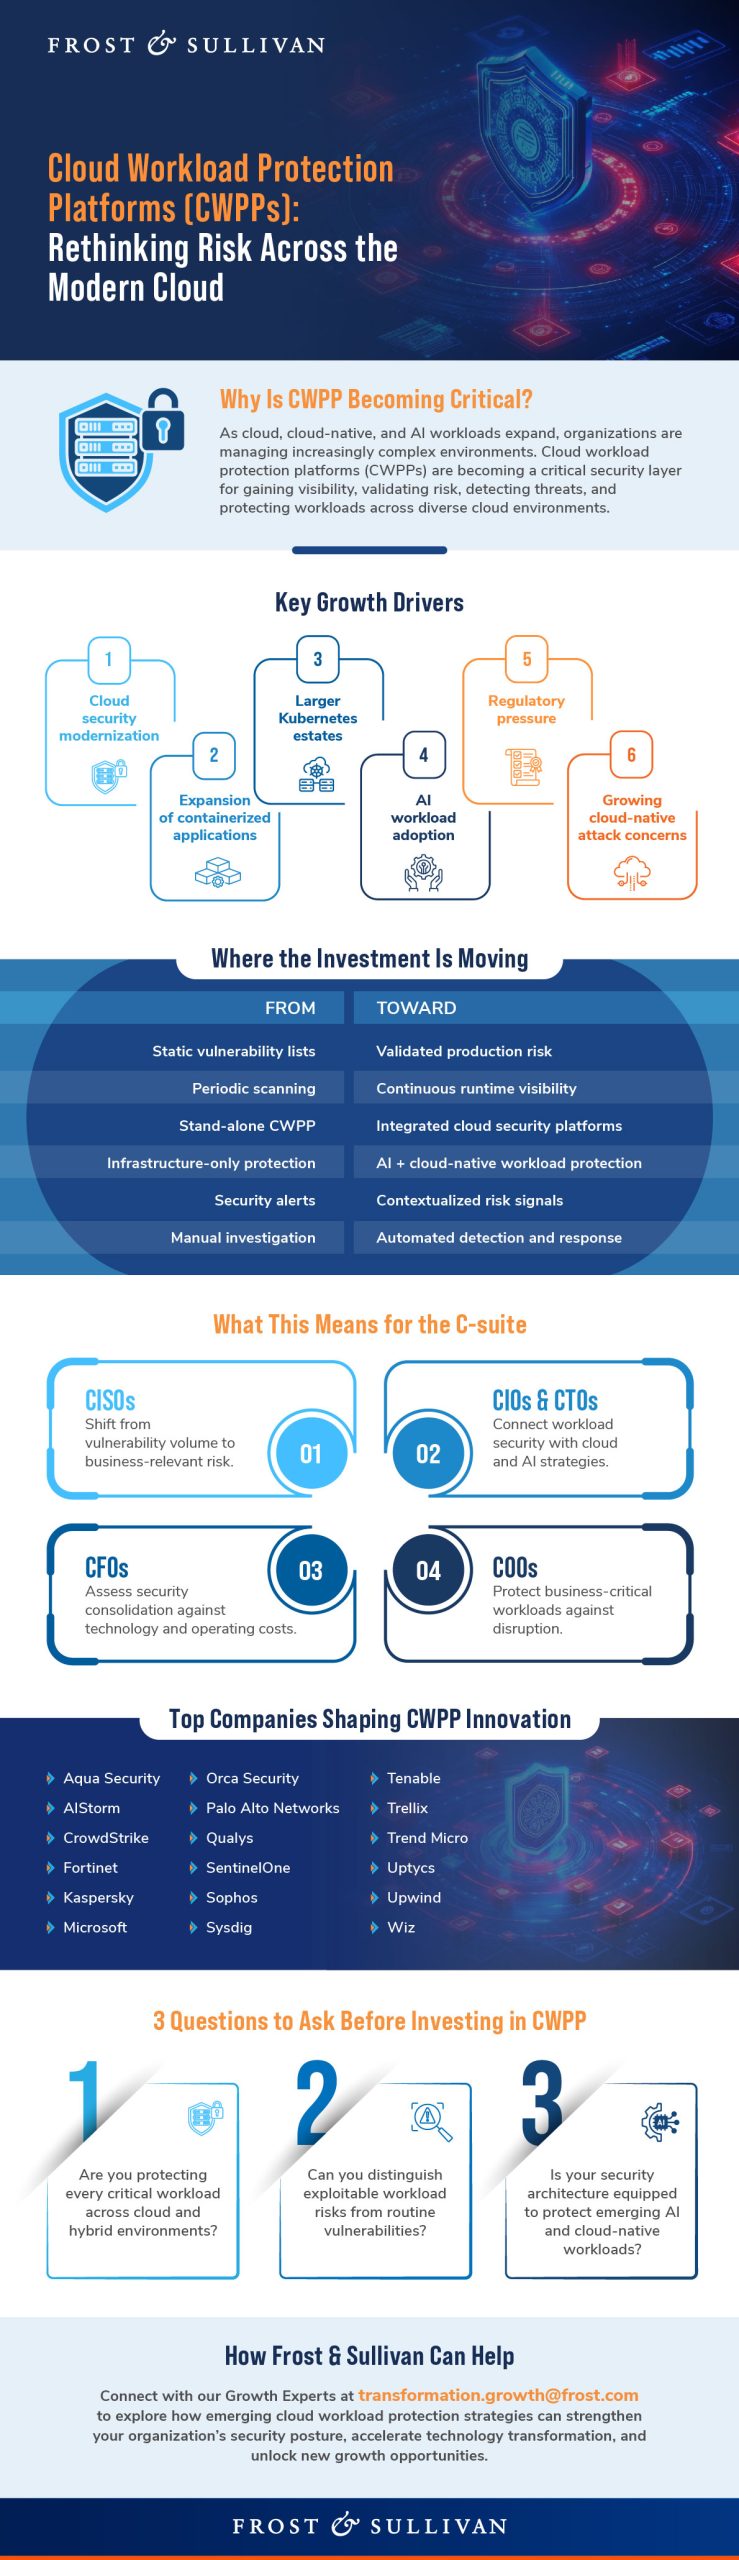
Cloud workload protection is moving beyond identifying vulnerabilities toward understanding which risks are actually exploitable in production. Frost & Sullivan’s assessment highlights how runtime telemetry, behavioral detection, cloud-native threat response, and platform convergence are reshaping CWPP as enterprises scale Kubernetes, containers, serverless, and AI workloads. With the market projected to reach approximately $7.95 billion in 2026, the ability to connect workload risk with runtime context, identity, data, and Security Operations Center (SOC) operations is becoming a key differentiator.
Cloud workload protection platforms (CWPPs) are becoming a critical security layer as enterprises expand across public, private, hybrid, multicloud, and edge environments. By combining workload visibility, vulnerability management, runtime protection, threat detection, and response, CWPPs are evolving to address increasingly dynamic workloads spanning containers, Kubernetes, serverless applications, and AI infrastructure.
Frost Radar™: Cloud Workload Protection Platforms, 2026, benchmarks leading vendors on Growth and Innovation, highlighting how providers are differentiating through runtime telemetry, cloud-native detection, platform convergence, AI workload security, and Security Operations Center (SOC) integration. The category is also extending into cloud detection and response and broader cloud-native application protection, reflecting a shift toward more connected approaches to workload security.
Key Takeaways
- Leading CWPPs are linking vulnerabilities with runtime behavior, exposure, identity, and reachability to prioritize active risks.
- Vendors are integrating workload protection with posture, identity, data, application, Application Programming Interface (API), and detection capabilities.
- AI models, retrieval-augmented generation (RAG) pipelines, agents, graphics processing units (GPUs), and model-serving infrastructure are expanding the workload security perimeter.
- CWPPs are increasingly connecting with Cloud Detection and Response (CDR), Extended Detection and Response (XDR), Security Information and Event Management (SIEM), SOAR (Security Orchestration, Automation, and Response) , and threat-hunting workflows.
- Platform vendors are emphasizing breadth and scale, while specialists are focusing on runtime depth, behavioral detection, and response.
Is your organization equipped to distinguish cloud vulnerabilities from business-critical risks?
Listen to our podcast episode on Top CWPP Vendors Shaping the Future of Cloud Runtime Security
What Is a Cloud Workload Protection Platform and Why Does it Matter for Organizations?
A cloud workload protection platform (CWPP) is a security solution designed to protect workloads across public, private, hybrid, multicloud, and edge environments. It provides visibility and protection across servers, virtual machines, containers, Kubernetes, serverless applications, and AI workloads, combining vulnerability management, runtime protection, threat detection, and response.
As workloads become more distributed and dynamic, traditional security approaches are making it harder to identify which vulnerabilities pose an immediate risk. CWPPs are helping organizations prioritize exploitable risks, detect threats at runtime, and respond faster, while integrating workload security with broader cloud and SOC environments.
How Does CWPP Work?
Cloud workload protection platform typically operates across five connected stages:
- Discover and Assess
CWPP identifies workloads across servers, virtual machines, containers, Kubernetes, serverless environments, and emerging AI infrastructure while assessing vulnerabilities, configurations, identities, and exposure. - Contextualize Risk
The platform correlates vulnerability and configuration findings with runtime activity, reachability, privileges, sensitive data, and business criticality to identify risks that could affect production workloads. - Monitor Runtime Activity
Runtime telemetry provides visibility into processes, network connections, workload behavior, and other activity, helping distinguish dormant vulnerabilities from active or exploited threats. - Detect and Investigate
Behavioral analytics and cloud-native threat detection identify suspicious activity and connect workload signals with broader cloud and SOC data. - Respond and Remediate
CWPP enables guided or automated actions such as virtual patching, workload isolation, process termination, and other response measures to contain threats and reduce risk.
Top 5 Strategic Imperatives Reshaping CWPP Landscape
- Runtime risk validation is becoming central to CWPP: CWPP is evolving from vulnerability identification toward validating whether risks are reachable, exploitable, active, or under attack.
- CWPP is converging with broader cloud security platforms: Integration with CNAPP, cloud detection and response, identity, data, API, application security, and SecOps is creating a more connected security architecture.
- Workload protection is spanning increasingly diverse environments: Virtual machines, containers, Kubernetes, serverless functions, cloud-managed services, and hybrid infrastructure are becoming part of a unified workload security landscape.
- Workload telemetry is moving into the SOC: Integration with cloud detection and response, endpoint and extended detection and response, SIEM, SOAR, and threat hunting is connecting workload activity with security operations.
- AI workloads are emerging as a new area of CWPP differentiation: AI assets, model-serving infrastructure, runtime behavior, sensitive data, plugins, agents, and Large Language Model (LLM) dependencies are expanding the scope of workload protection.
Who Is Leading the CWPP Landscape?
Frost & Sullivan’s Frost Radar™ evaluates CWPP vendors across Growth and Innovation, highlighting companies differentiating through technology capabilities, platform breadth, runtime depth, and growth potential. The 2026 analysis reveals several distinct competitive approaches.
| Vendor | Key Differentiators |
| CrowdStrike | Runtime telemetry, agent-based and agentless visibility, container and Kubernetes protection, CDR, and SOC integration |
| Microsoft | Multicloud workload protection, runtime detection, eBPF (Extended Berkeley Packet Filter), AI security, and Defender XDR/Sentinel integration. |
| Palo Alto Networks | Code-to-cloud-to-SOC protection, cloud runtime security, CDR, and Cortex platform integration |
| Wiz | Security Graph, attack-path analysis, workload context, identity, exposure, data, and runtime correlation |
Download the Full Analysis to Explore In-depth Details of All CWPP Innovators
Top 3 Three Growth Opportunities Emerging Across CWPP
- Runtime-informed Risk Prioritization
Organizations are facing large volumes of vulnerabilities and configuration findings. Vendors that can determine which risks are active, reachable, exploitable, or connected to sensitive assets can help customers reduce alert fatigue and focus remediation resources. Runtime telemetry is therefore becoming a source of competitive differentiation rather than simply another monitoring capability.
- AI Workload Protection
AI applications, agents, graphics processing unit (GPU) infrastructure, and model-serving environments are creating a new workload security segment. Cloud Workload Protection Platform providers can expand their platforms to protect AI infrastructure, models, identities, APIs, data flows, and runtime behavior, while cloud and consulting partners can support secure AI deployment and managed protection.
- Managed Cloud Workload Security
Hybrid and multicloud environments can be difficult to operate with internal resources alone. This is creating opportunities for managed security service providers (MSSPs), managed detection and response (MDR) providers, cloud partners, and systems integrators (SIs) to deliver workload monitoring, threat hunting, incident response, remediation, and policy management as managed services.
According to Frost & Sullivan, the CWPP landscape is evolving beyond traditional vulnerability management toward runtime-informed risk prioritization, AI workload protection, and managed cloud workload security. These emerging opportunities are reflecting the growing complexity of cloud environments and are creating new avenues for vendors and ecosystem partners to differentiate through deeper runtime intelligence, AI security capabilities, and specialized managed services.
What Should Security Leaders Look for in a CWPP?
The competitive landscape suggests that organizations should evaluate Cloud Workload Protection Platforms against more than vulnerability coverage.
Key evaluation criteria include:
- Runtime depth: Can the platform understand what is actually happening inside production workloads?
- Exploit validation: Can it distinguish exploitable risks from theoretical vulnerabilities?
- Kubernetes and container protection: Does it provide granular visibility and controls across cloud-native environments?
- Identity and data context: Can workload risk be correlated with permissions and sensitive data?
- Cloud-to-SOC integration: Can workload events feed directly into investigation and response workflows?
- AI workload protection: Can the platform secure AI infrastructure, models, agents, APIs, and data flows?
- Platform convergence: Can organizations consolidate workload, posture, identity, application, and data security capabilities?
- Response automation: Can teams isolate workloads, terminate malicious processes, or initiate remediation directly from security workflows?
The strongest platforms are increasingly combining these capabilities rather than treating them as isolated functions.
Best Practices for Technology Leaders Securing Cloud Workload
- Correlate workload vulnerabilities, misconfigurations, identities, exposure, sensitive data, and runtime activity to prioritize production risks.
- Combine agentless discovery with runtime telemetry to distinguish dormant vulnerabilities from active, exposed threats and reduce alert noise.
- Support virtual patching, workload isolation, process termination, and automated response with appropriate approval controls and rollback procedures.
Frequently Asked Questions (FAQs): Cloud Workload Protection
1. What is a Cloud Workload Protection Platform (CWPP) in cybersecurity?
A Cloud Workload Protection Platform (CWPP) is a security solution designed to protect workloads across public, private, hybrid, multicloud, and edge environments. It combines workload visibility, vulnerability management, runtime protection, threat detection, and response across servers, virtual machines, containers, Kubernetes, serverless applications, and emerging AI workloads.
2. Why is runtime protection important for CWPP?
Runtime protection helps security teams understand what is actually happening within production workloads. By analyzing runtime behavior, processes, network activity, reachability, and privileges, CWPPs can help distinguish dormant vulnerabilities from risks that are active, exposed, or being exploited, enabling more focused detection and response.
3. How is AI changing cloud workload protection?
The expansion of AI applications is creating new workload security requirements. Models, AI agents, retrieval-augmented generation (RAG) pipelines, GPU-enabled infrastructure, and model-serving environments are becoming part of the enterprise workload estate. CWPP providers are therefore extending protection to AI assets, runtime behavior, identities, Application Programming Interfaces (APIs), data flows, and application dependencies.
4. Which companies are leading the CWPP landscape?
According to Frost & Sullivan’s 2026 Frost Radar™, CrowdStrike, Microsoft, Palo Alto Networks, Wiz, Upwind, and Sysdig are among the leading vendors. These providers are differentiating through varying combinations of runtime protection, cloud-native security, platform convergence, AI workload protection, threat detection, and SOC integration.
5. How is CWPP evolving beyond traditional vulnerability management?
Cloud workload security is evolving from identifying vulnerabilities toward understanding their actual risk in production. Runtime telemetry, exploitability validation, attack-path analysis, behavioral detection, and guided response are enabling security teams to prioritize risks based on their potential impact rather than vulnerability severity alone.
6. How does CWPP integrate with the broader cloud security ecosystem?
Modern CWPP platforms are increasingly becoming part of broader cloud security architectures. They can connect workload telemetry with Cloud-native Application Protection Platforms (CNAPP), Cloud Detection and Response (CDR), identity, data, API, application security, and SecOps capabilities to create a more connected view of cloud risk.
7. What should organizations consider when evaluating a CWPP solution?
Organizations should consider the platform’s ability to provide comprehensive workload visibility, runtime context, exploitability validation, cloud-native and hybrid protection, and integration with existing security operations. Support for emerging AI workloads and the ability to connect workload risks with identity, exposure, data, and business context are also becoming important differentiators.
Ready to Lead the Transformation?
- Schedule a Growth Strategy Dialog: Align your growth roadmap with Frost & Sullivan’s Visionary Growth Pipeline™ Dialog.
- Engage with Growth Experts: Co-design AI-enabled, data-driven operating models that scale industry-specific and commercial impact.
- Showcase Your Transformational Leadership: Position your organization as a transformation leader through Frost & Sullivan’s Transformational Growth Leadership platform.
- Join the Growth Council: Collaborate with industry leaders shaping the future of your ecosystem.
- Explore Best Practices Recognition: Be recognized for excellence in growth strategy, execution, and customer impact.
- Benchmark Your Industry Positioning on the Frost Radar™: Benchmark your growth performance and innovation strength against industry competitors.
- Tell Your Story: Accelerate awareness, engagement, and revenue growth through integrated brand and demand generation strategies.